
Open this photo in gallery:
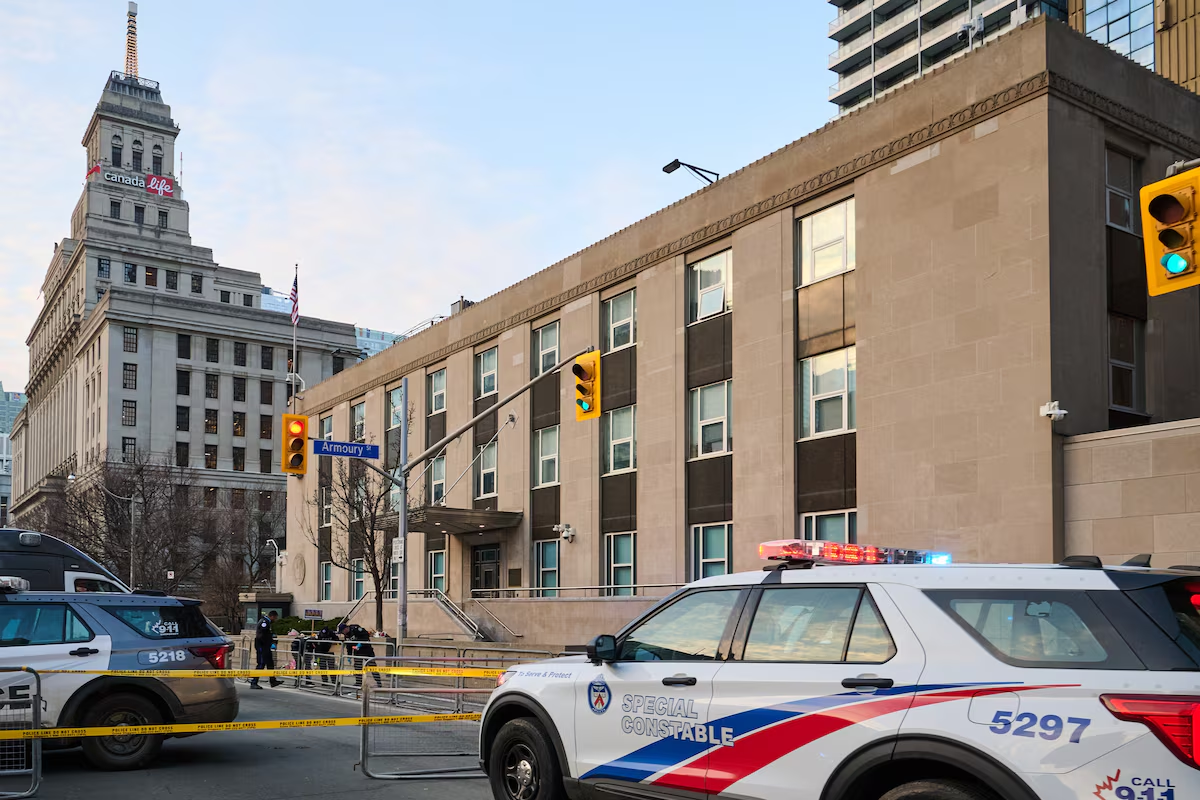
Police survey the scene after shots were fired at the U.S. consulate in Toronto on March 10.Sammy Kogan/The Globe and Mail
Investigations into a series of shootings in Toronto have been stymied because a key cellphone that was seized in connection with the case is running on a privacy-focused operating system and investigators have so far been unable to unlock the device, according to a police source.
Police believe the cellphone may contain communications and other data that could point to those responsible for ordering the shootings, including the March attack on the U.S. consulate, the source added.
In June, police launched a series of raids in response to the attack, as well as others on synagogues and local businesses in Toronto. An officer was killed in those operations and several suspects were arrested.
The phone operates on a little-known and highly secure operating system called GrapheneOS, reputed to be one of the most difficult to penetrate in the world, the source said. The Globe and Mail is not identifying the source, who is not authorized to discuss the case.
GrapheneOS is available for users to download and install for free and is based on the Android Open Source Project, which allows developers to modify elements of the basic Android framework. GrapheneOS was created by Toronto programmer Daniel Micay.
Shooter-for-hire attacks linked to Toronto police constable’s licence plate searches, Project South documents allege
The police theory is that these shootings, which targeted buildings, businesses and other property, are the work of a loose network of mercenary gunmen unconnected to their targets, hired like gig workers via encrypted messages.
While GrapheneOS represents a uniquely difficult challenge for law enforcement, security features built into other technology also pose a serious problem. Newly released models of the iPhone, for example, can be complicated for investigators to crack, as are messaging apps such as Signal and WhatsApp, which offer users encryption and auto-delete functions.
The Toronto Police Service said that while it cannot comment on the status of a particular forensic examination, its officers are seeing encrypted technology used to plan a range of criminal activity.
Toronto Police Chief Myron Demkiw has publicly expressed his support for new federal legislation currently before Parliament, Bill C-22, that in his view would assist investigators who encounter encrypted information.
The controversial bill would force electronic service providers to facilitate the interception of data to help police and intelligence services with investigations. But it has been opposed by tech companies and advocates for civil liberties.
“As criminals increasingly use encrypted technology to facilitate serious criminal activity, law enforcement needs the appropriate lawful tools to keep pace,” said Stephanie Sayer, a Toronto police spokesperson.
Lawful-access bill could threaten encryption, deter investment, Chamber of Commerce warns
The GrapheneOS project said in a statement issued through its lawyers that, like any technology, it can be used for legitimate purposes or be misused by those involved in criminal activity. The project condemns all acts of violence, it said.
It also said it has not received any kind of request for assistance from a Canadian police force in recent months. If it were to receive such a request, the operating system is designed to make that type of assistance impossible, according to its statement.
“GrapheneOS is designed such that the project cannot bypass its own security protections. There are no backdoors, master keys, or remote access capabilities,” the statement said.
“This is a deliberate architectural choice: security that relies on the benevolence of the developer is not security at all.”
Experts say police are now able to crack many of the most popular cellphone configurations, thanks largely to the help of companies that specialize in digital forensics.
But GrapheneOS appears to be a different case.
It bills itself as a privacy- and security-focused operating system designed to protect against data theft, surveillance and security vulnerabilities. It has been praised by Edward Snowden, the former government contractor who revealed U.S. mass surveillance capabilities and was later charged with espionage.
Opinion: Shooters-for-hire network in Toronto shows a new front in the fight against terror financing
Mr. Micay, who declined an interview request but responded to questions through his lawyer, started work in this domain more than a decade ago when he was 20 years old.
He eventually co-founded a company called Copperhead along with two others that later dissolved in a legal dispute that’s still before Ontario’s Superior Court. But the project continues as GrapheneOS, which is a registered non-profit in Canada.
GrapheneOS has about 350,000 to 400,000 users, according to its website, compared with the billion or more people using Apple’s standard iPhone operating system.
It’s funded by donations, which it says have been substantial, according to a post on its website earlier this year connected to a WIRED magazine article about the legal fight over Copperhead. The same post said that Mr. Micay’s income comes solely from sponsors on the GitHub platform, and that the GrapheneOS Foundation “is a non-profit and no one is getting rich from it.”
Mr. Micay said in court documents that he still contributes to the project but stepped down from the lead-developer role in 2023. The GrapheneOS Foundation lists Mr. Micay as a director, with a registered office address in Toronto.
Toronto police charge two suspects in U.S. consulate shooting
In its statement to The Globe, GrapheneOS said its system, like other operating systems, has protections against unauthorized access.
“In cases where individuals are attempting to access a device without the owner’s PIN or password, operating systems have no way of knowing whether an ‘unauthorized’ access attempt is valid,” the statement said. “The project does not distinguish between ‘good’ and ‘bad’ actors, because such distinctions are inherently subjective and subject to abuse.”
The tradeoff to using this kind of high-security operating system is that it’s less convenient, so few people do it, said David Lie, a professor of computer and electrical engineering at the University of Toronto. But Prof. Lie said there’s no legal prohibition against using a privacy-focused operating system, and in some cases, it may be essential for political dissidents, activists and journalists.
Last year, an American political activist who had GrapheneOS installed on his phone was stopped at a U.S. border entry point. He was asked to provide the code to unlock the device and instead provided what’s known as a duress PIN, which triggered a mechanism that wiped his phone clean. He has since been charged with destroying property to prevent seizure.
GrapheneOS issued a post on social media earlier this year defending the duress PIN, which it described as one relatively minor feature in its suite of defences.
“GrapheneOS is completely legal. We have no obligation to weaken any of the security protections it provides,” the post said. “Laws attempting to make it illegal or require weakening the security would be unconstitutional.”
Crown stays charges against man accused in GFL shootings case
Bill Budington, senior staff technologist at the Electronic Frontier Foundation, an organization that defends civil liberties in the digital sphere, said GrapheneOS’s effectiveness stems from the decision to treat any function that might compromise security as an opt-in choice for users.
“They’ve prioritized fixing areas of the operating system that will increase what’s called your attack surface, the places where an attacker can gain access to your device,” Mr. Budington said.
Mr. Budington said GrapheneOS is portrayed at times as a tool that appeals to bad actors, but that’s not accurate, in his view.
“There are a number of reasons why someone might want to use GrapheneOS rather than the base Android, and it has nothing at all to do with whether they’re committing crimes,” Mr. Budington said. “There are plenty of people using these operating systems because they don’t want [to give away] access to their devices.”
The technology’s appeal to criminal groups contributed to the breakdown of the Copperhead company in 2018, according to an affidavit filed by Mr. Micay.
He said his former business partner, James Donaldson, “decided to pursue business deals with criminal organizations.” The affidavit names a Canadian company called Phantom Secure, whose CEO was sentenced in the U.S. to nine years in prison for selling supposedly secure cellphones to transnational drug cartels.
Spate of police deaths sparks calls for action as officer mourned at Toronto funeral
Mr. Micay says in the court documents that he was uncomfortable with the proposals, which included making changes to the operating system’s security protocols and initiating remote updating systems that would allow third parties to have access to users’ phones.
He instead chose to delete part of the company’s technology to protect its users from interference from criminal organizations, the documents state. He subsequently ended his relationship with Mr. Donaldson, who is not connected to the GrapheneOS project.
Mr. Donaldson and Copperhead reject that version of events and said in their filings that they never pursued business deals with criminal organizations. They said the business relationship broke down because of Mr. Micay’s “belligerence and refusal to deal with Mr. Donaldson.”
Canadian authorities have long sought a law that would force electronic service providers to grant access to data in a timely manner, a provision some have compared to requiring an open electronic backdoor. Bill C-22, currently before Parliament, may finally grant law enforcement much of what they have been seeking. But how to strike a balance on privacy and security is the subject of intense debate.
Citizen Lab at the University of Toronto called the bill’s data-retention requirements, which would mandate electronic service providers keep detailed data of nearly every Canadian for a year, revealing their movements and who they contacted, “almost certainly unconstitutional.”
Major tech companies such as Signal, which provides secure messaging, and DuckDuckGo, a privacy-focused search engine, have said they would withdraw from Canada if they were forced to reveal or retain user data that compromises users’ privacy.
Although it was once difficult for law enforcement to search locked cellphones, it’s now relatively routine, said Alain Filotto, a retired RCMP officer who now runs a digital-forensics company in B.C.
He said there are two major software companies that supply digital-forensic solutions to police: Cellebrite, with headquarters in Virginia, and Magnet Forensics, based in Waterloo, Ont.
“They can pretty much unlock any phone,” Mr. Filotto said.
Most major police forces subscribe to services from one or both of these companies, Mr. Filotto said. And when a digital-forensic search of a device is authorized, they essentially plug the phone into the software and make a digital copy of its contents.
Neither Cellebrite nor Magnet Forensics would comment on whether it has ever succeeded in extracting digital data from a phone running GrapheneOS.
The RCMP and the FBI also declined to comment on that question.
With research by Stephanie Chambers